EU Regulation: Cockpit, ICT Register, AI Inventory
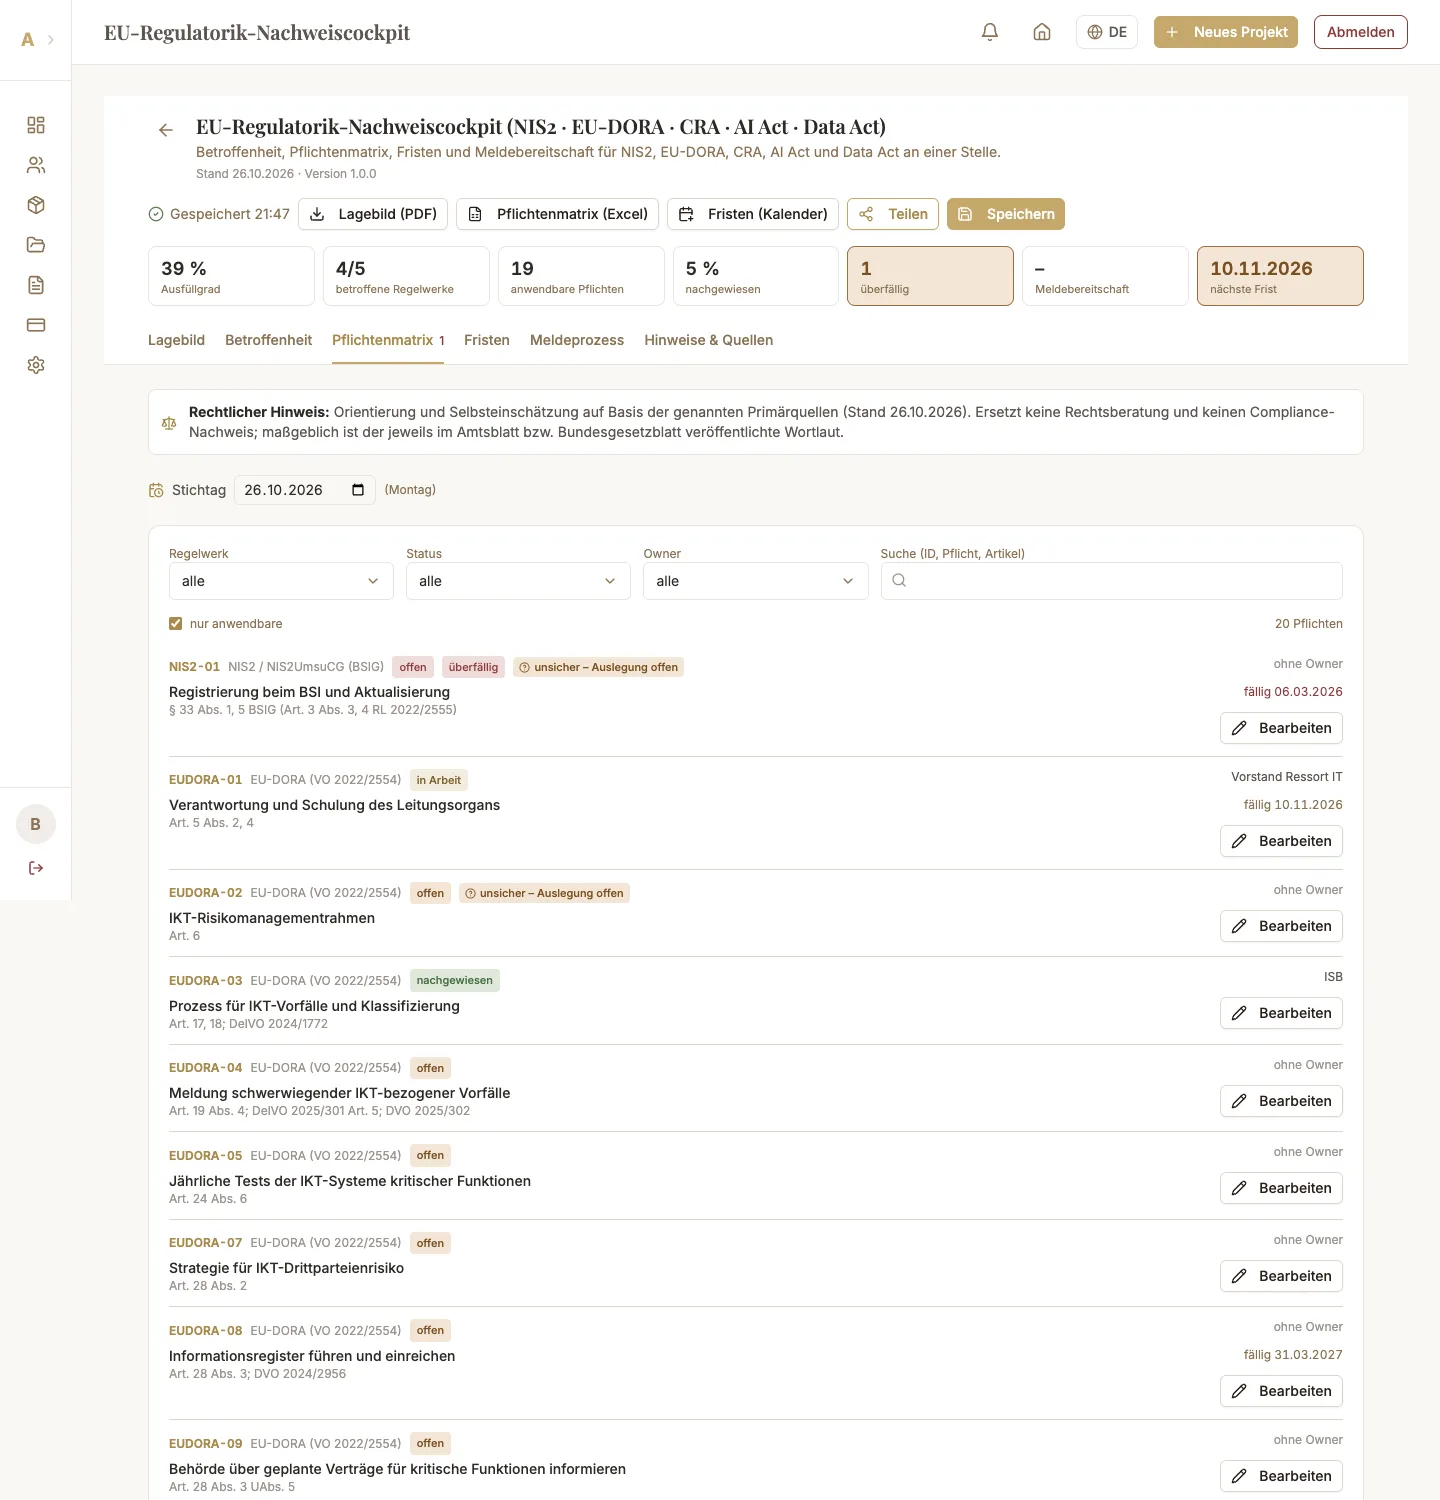
For EU regulation there are three connected tools: the EU regulatory evidence cockpit (NIS2, EU-DORA, Cyber Resilience Act, EU AI Act, Data Act), the ICT third-party register under EU-DORA and the AI inventory with AI Act classification. The vendor assessment additionally checks vendors against EU-DORA and NIS2.
Regulatory cockpit
Clarify applicability
Answer a few questions per regulation; existing results from the readiness checks and the AI inventory are offered as suggestions.
Maintain obligations
For each obligation record owner, evidence and status (open, in progress, evidenced, not applicable with reason).
Deadlines and reporting
The deadline calendar shows fixed and recurring deadlines (ICS export). The reporting drill walks through an incident and shows which report would be due when.
For management there is a PDF briefing with applicability, fulfilment per regulation, open obligations and next deadlines.
ICT third-party register
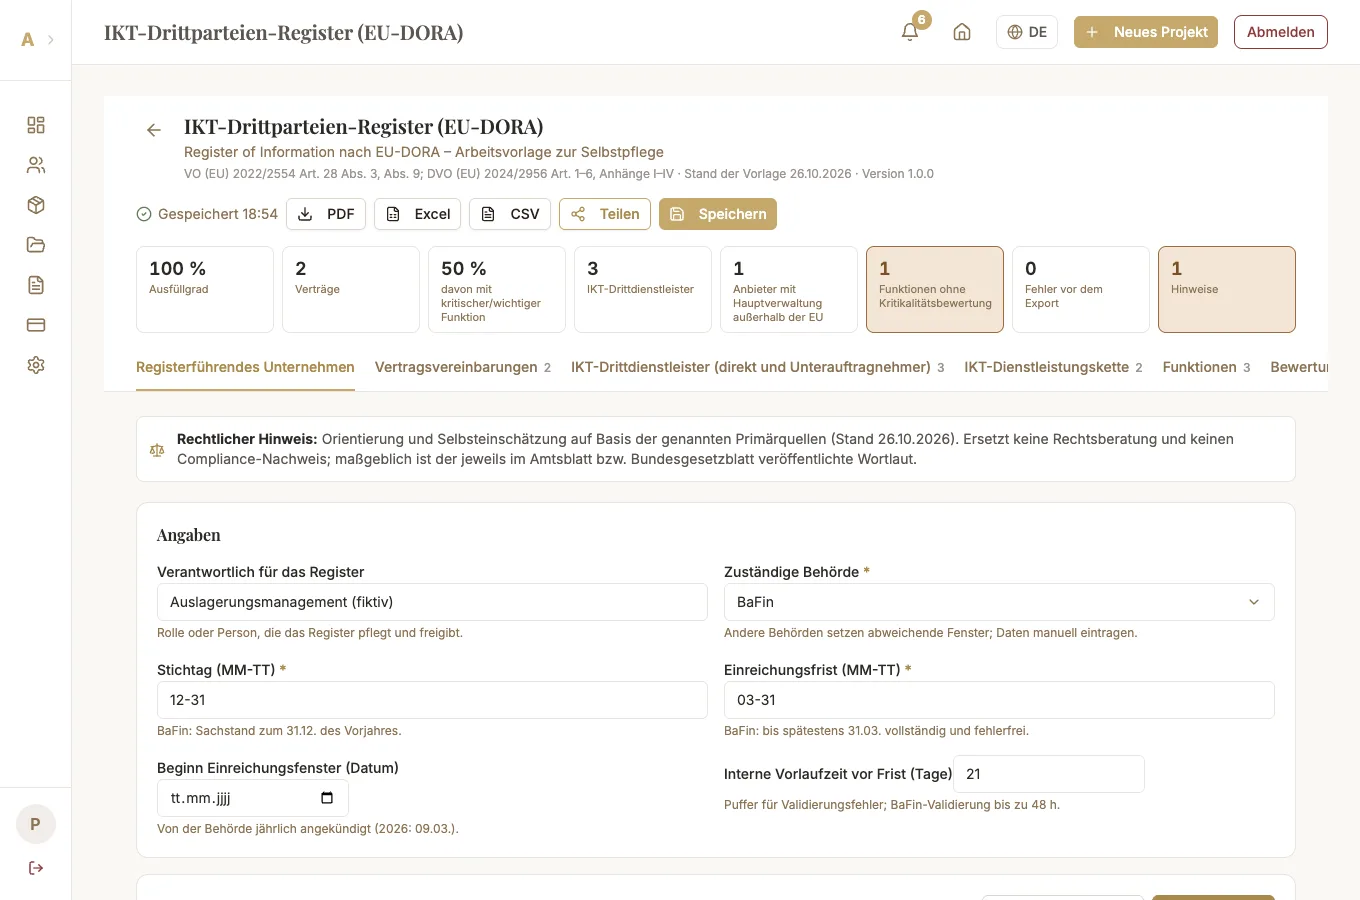
The register follows the EU-DORA register of information. Plausibility rules point out gaps (e.g. a critical function without an exit plan). The Excel export is a working template for maintenance – not a submission-ready reporting format. Data from the vendor assessment can be taken over without double entry; the CSV import reads existing lists.
AI inventory
Each AI system is recorded with purpose, role (e.g. provider or deployer) and model, and assigned to an AI Act risk class through a guided classification. The obligations with article and deadline follow from it. Use cases from the AI use case prioritisation can be taken over via CSV.